AI lifecycle and operating responsibility
Retire an AI Workflow Without Abandoning Its Work
A Retirement Record for closing intake, assigning outstanding obligations and demonstrating a safe handover when an AI workflow ends.
Turning off an AI workflow does not decide who finishes the work it leaves behind.
A business may have good reasons to retire an automation. The process changed. A limited pilot served its purpose. A supplier relationship ended. The team found a simpler way to deliver the outcome. Keeping a workflow alive merely because someone once built it is not a strategy.
But retirement is not just the opposite of deployment. A workflow can stop receiving new requests while earlier work, customer commitments and downstream records remain active. The owner needs a way to close the system without quietly dropping the business obligation.
I would treat planned retirement as an operating decision with its own evidence. My proposed Retirement Record names what will stop, what still exists, who receives it and what demonstrates that the transition is complete. It is not a private implementation specification or a promise that a checklist eliminates every risk.
Retirement is a lifecycle decision
NIST's AI Risk Management Framework Core includes safe decommissioning and phasing out AI systems in GOVERN 1.7. That is voluntary risk-management guidance, not a universal legal shutdown procedure. Its relevance is straightforward: the end of a system's life belongs inside governance, rather than outside it.1
The Australian National AI Centre's implementation guidance makes the practical concerns more explicit. Section 6.2 addresses retirement reasons, responsible people, dependencies, transition planning, records, notice and alternatives. I use it as a useful independent reference, not as a statement that Australian requirements apply to every reader.2
A planned retirement also differs from emergency containment. If there is an active security incident or a dangerous action, the authorized response team may need to restrict access immediately. Do not wait for a tidy retirement exercise to contain immediate harm. Afterwards, the organization still needs to reconcile outstanding work and explain what happened.
Nor is retirement necessarily failure. The useful outcome might survive in a simpler manual process or another approved service. The question is not whether the old automation deserves to continue. It is whether the business can account for what it accepted while that automation was operating.
Stopping intake is not finishing the backlog
Consider an explicitly synthetic example. A small maintenance business used an AI-assisted workflow to prepare renewal reminders. It is moving those reminders into its existing customer-management process. The owner disables the old intake form and assumes the migration is done.
I would inspect three kinds of work before accepting that conclusion. Some requests may be waiting for their turn. Others may already be in progress. Some reminders may already have been delivered and could still produce replies that need attention. These are questions about the actual implementation, not assertions that every workflow contains all three.
A technical pause should not be mistaken for a final closure. Google Cloud Tasks, for example, documents that a paused queue can still receive tasks and that its backlog is processed when the queue resumes. That is one service's behavior, not a claim about every queue or a guarantee about cancelling work already executing.3
The practical lesson I draw is to inspect the actual controls separately. What stops new work entering? What stops a scheduled trigger? Which work can still act? What would happen if someone resumed the old path later? A single disabled switch does not answer every one of those questions.
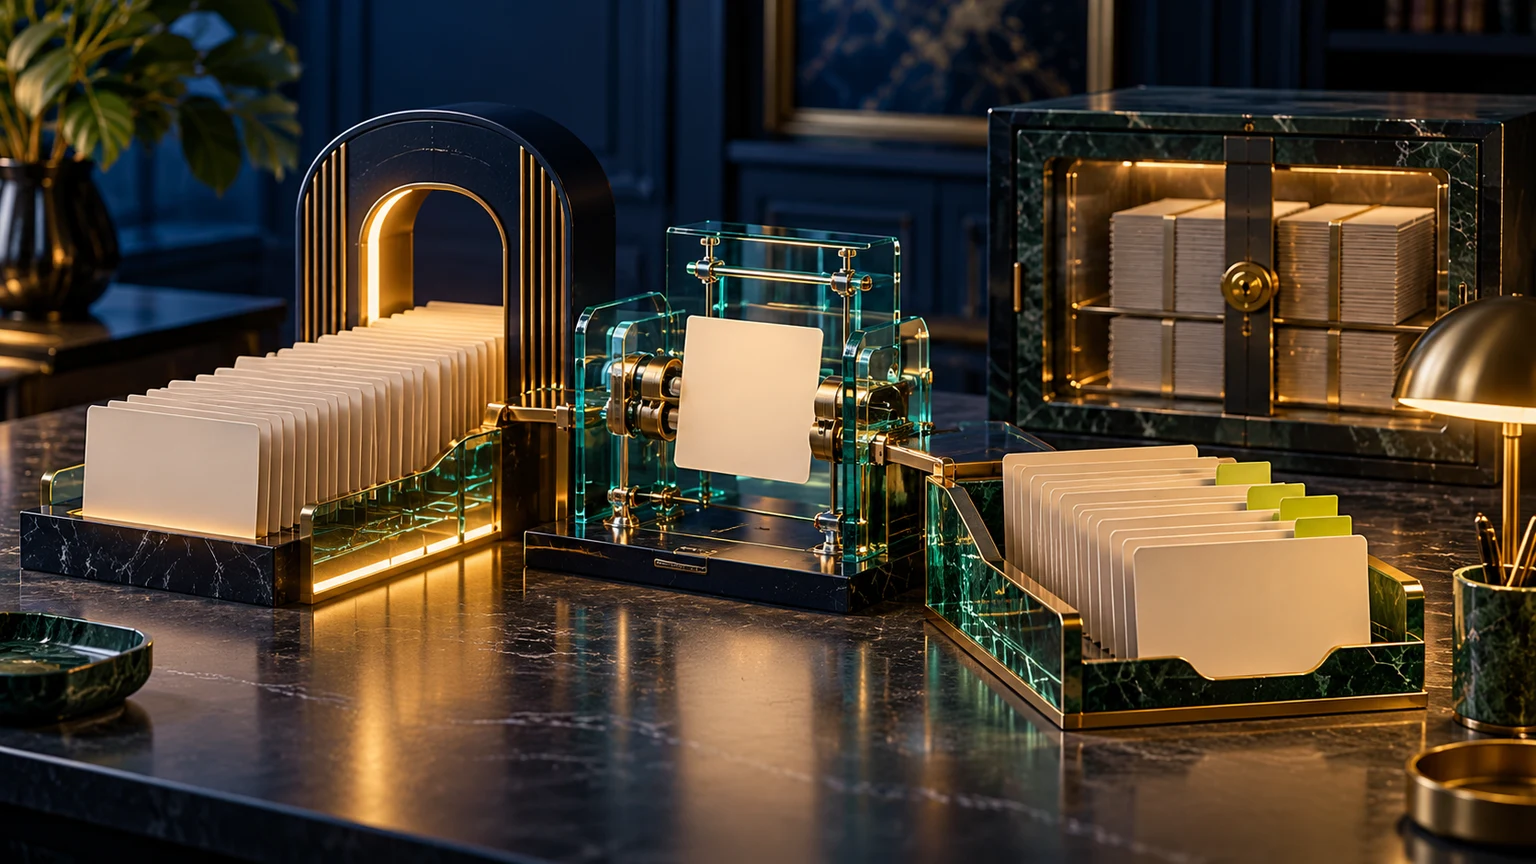
Original conceptual illustration. The three work states are an inspection model, not a claim about a particular product's storage or execution behavior.
Assign a disposition, not a disappearance
In the fictional maintenance business, I would give each outstanding renewal an explicit disposition. Some may move to the replacement process. Some may need manual review because the underlying customer details changed. Others may be cancelled by an authorized owner because the service is no longer offered. Cancellation should include any notice or follow-up the business actually owes.
Do not blindly drain the backlog just to make a dashboard empty. Old instructions may no longer be appropriate, and a queued message may no longer be wanted. The decision is what should happen now, not how to force every earlier task into a completed state.
Delivered work needs a receiving path too. If a customer replies to an old reminder after the automation retires, where does that reply go? If the old workflow created a record in another business system, which team owns the record from now on? Retirement of the producer is not automatically retirement of its outputs.
These are ownership questions before they are software choices. A replacement can be manual and still be a real operating path; an impressive new platform can still be an unowned destination. The receiving team needs the authority, access and capacity to handle the obligations it accepts.
Write one Retirement Record
My version has five commitments. They should be short enough for the process owner and implementer to review together:
- Boundary: name the workflow, why it is retiring and exactly which intake, schedule and action paths are included.
- Work: identify queued, in-progress and delivered-but-still-open obligations; record a disposition and owner for each relevant class.
- Successor: name the receiving process, its capacity, the effective handover point and the people who need to know.
- Evidence: specify the decisions and records that must remain accessible, under the approved retention, access and deletion rules.
- Closure: define the observation and sign-off that show the old path no longer accepts or acts unexpectedly, and assign residual questions to someone.
The evidence commitment is not an instruction to keep everything forever. Follow the organization's obligations and approved lifecycle. Some information must be retained; other information should be removed. Do not erase the explanation of an unresolved customer decision merely to make decommissioning look clean, and do not preserve unnecessary private data merely because archiving feels safer.
Access removal also deserves a scoped plan. An old integration's credentials, schedules or service identities may be shared with other work. The implementer should verify the dependency before changing it. “Remove access” is an authorized change to a defined target, not permission to disable every account connected to the old service.
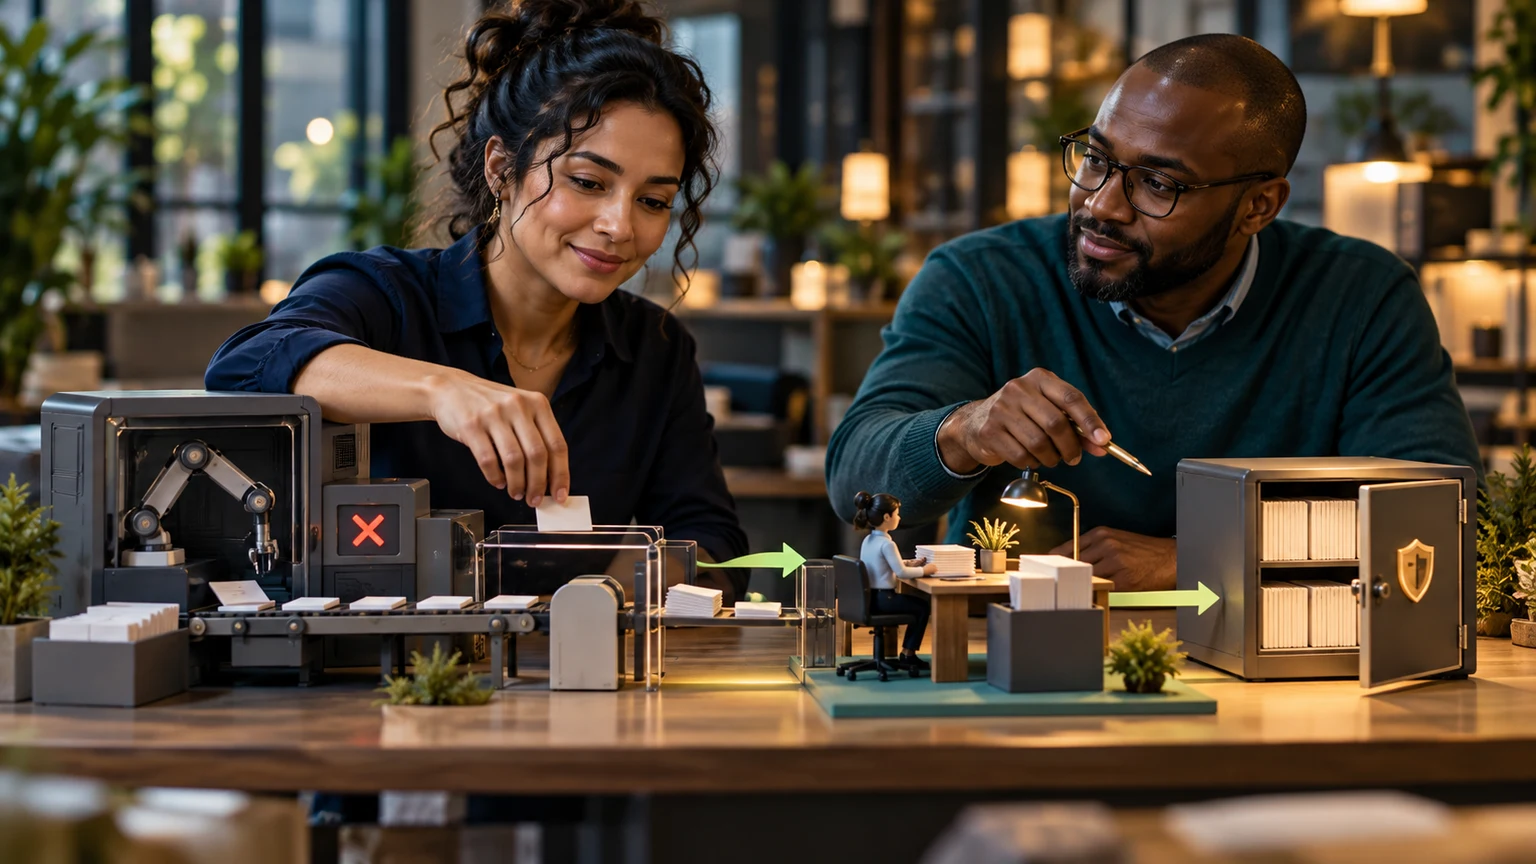
Fictional tabletop rehearsal, not evidence of a measured customer result. Test with synthetic records and approved change procedures.
Rehearse the day after retirement
Before the planned change, I would rehearse three fictional cases: one request waiting before the cutoff, one action already in progress and one reply arriving after the cutoff. Ask the receiving person to locate each case, explain its disposition and identify the next accountable action.
Check the old entry points as well as the replacement. Does a scheduled path still create work? Can an old link make a promise the business no longer supports? Would a later restore or an accidental resume reactivate the old behavior? Establish what the team can verify, and write down what remains uncertain.
The observation period should fit the consequence and timing of the work. There is no universal number of quiet hours that proves retirement. A daily reminder and an annual renewal have different horizons. Name the evidence needed rather than invent a calendar threshold that makes every workflow appear safe.
This method does not prove that all data copies are gone or that every obligation has been discovered. It creates a concrete basis for a narrower acceptance decision, with remaining uncertainty attached to an owner. My preferred ending is not “we switched it off.” It is “we know what stopped, what continues and who is responsible now.”
Research Record
References and Evidence
The scenario and rehearsal are explicitly synthetic. The practical artifact is my operating interpretation, not a measured customer result, a complete assurance or security audit, a legal determination or private CPF implementation. The illustrations are original conceptual artwork, not evidence of actual business results.
- AI RMF Core: GOVERN 1.7Voluntary risk-management framework · NIST AI RMF 1.0; accessed October 26, 2026
Includes safe decommissioning and phasing out AI systems. Voluntary guidance; does not establish a universal shutdown procedure or certify this proposed artifact.
- Guidance for AI adoption: implementation guidanceGovernment implementation guidance · Australian National AI Centre; section 6.2; accessed October 26, 2026
Addresses decommissioning reasons, owners, dependencies, records, notice and alternatives. This Australian guidance is used as a reference, not a statement of legal applicability to every reader.
- Manage queues and tasks: Pause or resume queuesProvider-specific operational documentation · Google Cloud Tasks; accessed October 26, 2026
Paused queues can still receive tasks and resume processing backlog later. Does not establish another service's behavior or cancellation of already executing work.